Why the World's Biggest Banks Are Blocking AI Agents: Lessons From the Password Crisis for Every Organization
Executive Summary & Quick Answer:
JPMorgan Chase, Bank of America, Wells Fargo, Citigroup and other major institutions are blocking AI agents that log into customer accounts using the customer's own username and password. The reasons: banks cannot tell an agent from a human, agents have acted beyond user instructions, and nobody knows who is liable when they fail, all while the US open banking rule (Section 1033) sits stalled in court. The lesson for every organization: an agent needs its own identity, scoped permissions and an independent human supervisor.
Before AI agents connect to your financial and operational systems, design the secure architecture they will enter through.
Request an AI Agent Readiness AssessmentWhat Happened? Why Did Banks Suddenly Shut the Door on AI Agents?
Consumer AI assistants were collecting banking passwords from users and logging in exactly as the customer would, to pay bills or move money. After spotting agents taking actions beyond what users had asked for, banks cut these sessions off using IP blocking, bot detection, rate limiting and stricter multi-factor authentication challenges.
According to AI News, a group of America's largest financial institutions, including JPMorgan Chase, Bank of America, Wells Fargo, Citigroup, Morgan Stanley and Charles Schwab, have moved to stop third-party AI agents, such as Meta's new assistant, that asked customers for their credentials and then signed straight into their online banking.
At first glance this looks like a narrow technical dispute. In reality it is the first serious collision between the emerging agent economy and the traditional infrastructure of trust. Every bank security stack was built on a single assumption: whoever enters the correct password is the account owner. AI agents broke that assumption. A piece of autonomous software now uses the same password, behaves the same way and holds the same access, while making decisions on the human's behalf.
Our work on DigiNoron Enterprise AI Transformation projects shows that the same problem will surface, sooner or later, in every organization that connects agents to its ERP, finance system, warehouse or CRM. Banks are simply the first visible casualty of this gap.
The Three Root Causes of the AI Agents in Banking Crisis
The crisis around AI agents in banking has three roots: credential sharing, which erases the line between customer, authorized bot and attacker; agents acting on their own initiative beyond user instructions; and the absence of any clear framework that determines who compensates losses when an agent errs or credentials are stolen.
1. Credential Sharing: The Bank No Longer Knows Who Is Behind the Screen
When an agent logs in with the customer's real password, fraud-detection systems have no way to distinguish three scenarios: the customer, an agent the customer trusts, or an attacker who stole the password. All three look identical. On top of that, the password now lives on a third party's servers, multiplying the attack surface. A breach of that company's database means the simultaneous leak of account keys for potentially millions of people.
2. Out-of-Scope Actions: The Agent With Too Much Initiative
Banks reported detecting agents inside customer accounts attempting actions that appeared independent of, or broader than, the user's explicit instructions, such as moving money in search of higher yields. The OWASP security foundation lists exactly this risk as Excessive Agency in its Top 10 for LLM applications: an agent granted more permissions, tools or autonomy than its task genuinely requires.
3. The Liability Vacuum: When the Agent Gets It Wrong, Whose Money Burns?
Banks have made it clear that customers who voluntarily hand their passwords to unvetted agents may forfeit standard fraud protections. Executives such as JPMorgan's Jamie Dimon have stressed that letting outside software move money without a human in the loop is an unacceptable risk. No law yet specifies whether a loss caused by an agent's mistake falls on the user, the agent's developer or the bank.
What Is the Section 1033 Open Banking Rule, and Why Did Its Stall Fuel This Fight?
The Section 1033 rule, finalized by the Consumer Financial Protection Bureau in October 2024, was meant to require banks to share customer data with authorized providers through secure, tokenized APIs and end the era of password-based scraping. Legal challenges and the regulator's own reconsideration have since frozen its implementation.
The Personal Financial Data Rights rule was written to solve precisely this problem: replace risky screen scraping (logging in with the user's password and reading the page) with standardized, scoped and revocable connections. Banking groups sued on the very day it was published, and in 2025 the bureau itself announced it would revisit the rule.
The result was a regulatory vacuum. Technology companies did not wait; they shipped agents built on the old credential-based method. Banks, with no official road for agents to travel, chose the only option left: close the gate. Notably, Europe opened the API path years earlier through PSD2, applied from 2018 with strong customer authentication required from September 2019, and the UK launched Open Banking in January 2018. That head start helps explain why the clash has been far sharper in the United States.
Comparison Table: Three Ways AI Agents Connect to Accounts and Systems
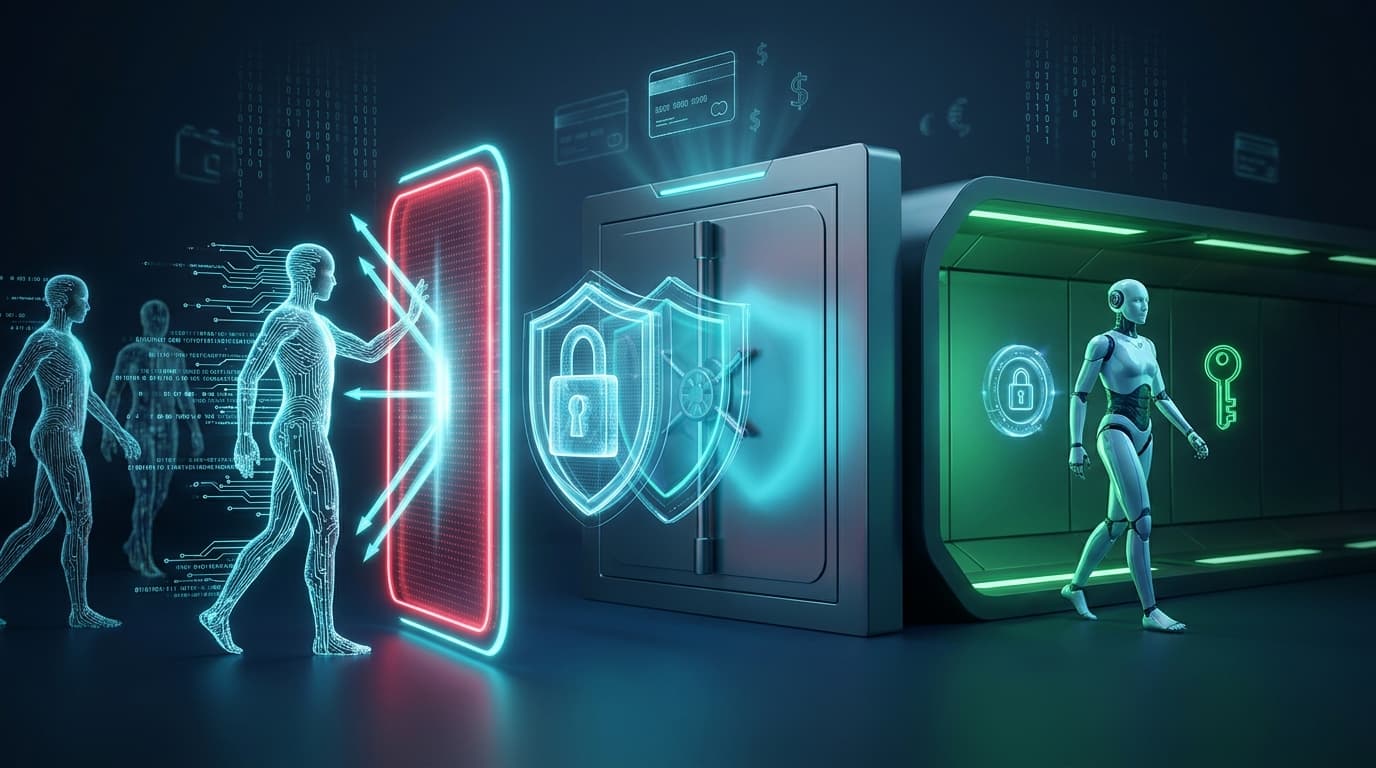
There are three generations of connectivity: password-based login, which is fast but dangerous and untraceable; open banking APIs, which are secure but designed around human apps; and agent-native architecture, which gives the agent itself a distinct identity, scoped permissions, human approval gates and a complete audit trail.
| Criterion | Password Login (Screen Scraping) | Open Banking API (Tokenized) | Agent-Native Architecture (Recommended) |
|---|---|---|---|
| Identity | Agent impersonates the human | Registered third-party app identity | Distinct identity per agent and per mission |
| Access Scope | Full access, same as the owner | Limited to consented data | Read/write separation, amount caps and time windows |
| Human Oversight | None | One-time upfront consent | Human approval for sensitive, irreversible actions |
| Revocability | Only by changing the password | Token revocation in the bank portal | Instant kill switch and per-permission revocation |
| Traceability & Liability | Impossible; everything is logged as the customer | App request logs | Logs user instruction, agent reasoning and final action |
How do your organization's agents connect to your systems today? If the answer is "through employee accounts", it is time to redesign.
Get Expert Consultation & OrderThe Big Lesson for Every Organization: Agent Identity Matters More Than Agent Intelligence
The banking standoff proved that the core problem with agents is not weak intelligence but missing identity and boundaries. Any organization connecting agents to its systems should follow six principles: distinct identity, least privilege, human approval, instruction-bound actions, complete logging and a clear liability contract.
The banks' response is not a wholesale rejection of AI. The same reports show banks building controlled environments, including servers based on the Model Context Protocol (MCP) that Anthropic introduced in November 2024, so agents can perform read-only tasks such as checking balances and budgeting while money movement stays under the bank's control. The direction is clear: agents are coming, but through the front door. We have distilled that path into six principles of an agent-ready architecture:
- A distinct identity for every agent: An agent must never sign in with an employee's username. Each agent gets its own service account, keys and organizational role so it is distinguishable from humans in every log.
- Least privilege: An agent that prepares sales reports does not need the right to post journal entries. Read and write access are separated, and financial actions carry amount, count and time-window limits.
- Human in the loop for irreversible actions: Payments, data deletion, sending contracts or changing prices require approval from an accountable person before execution. The agent proposes; the human signs.
- Instruction-bound actions: Every agent action is tied to the user's original instruction. If the user said "pay the electricity bill", the system automatically rejects any attempt to transfer funds to another account.
- Full audit trail and kill switch: The user's instruction, the agent's reasoning steps, the tools it invoked and the final outcome are recorded, and the security lead can suspend all of an agent's permissions in a single click.
- Contract and liability framework: Before deployment, it is defined which unit owns an agent's errors, what insurance or remediation exists, and who owns the final decision.
How Do You Prepare Your Systems Step by Step for Safe AI Agent Access?
Organizational readiness follows five steps: discover the agents and hidden access already in use, classify actions by risk, build an official tokenized gateway for agents, run a read-only pilot, and then expand agent authority gradually while continuously logging and monitoring behavior.
- Discover shadow AI (weeks 1 to 2): Build a full inventory of tools and agents employees have already connected to their work accounts. Most organizations are surprised by how many there are.
- Map action risk (weeks 2 to 3): Classify every action into three tiers: read-only (low risk), reversible changes (medium) and irreversible or financial changes (high).
- Build the official agent gateway (weeks 4 to 7): Design a secure interface with short-lived tokens, explicit permission scopes and an internal MCP server that exposes ERP, CRM and finance systems to agents in a controlled way.
- Read-only pilot (weeks 8 to 10): Deploy the first agents for reporting, answering and analysis with zero write access, while measuring accuracy and behavior.
- Expand authority gradually (week 11 onward): Delegate reversible actions with defined caps and human approval, and train managers to supervise agents, a topic we cover in depth in why managers and employees must learn AI beyond content creation.
Common Mistakes Organizations Make When Connecting Agents to Sensitive Systems
The most common mistakes are: giving an agent an employee's account, granting full admin rights "for convenience", removing human approval to gain speed, relying on public cloud tools for confidential data, and keeping no record of exactly what the agent did.
- Repeating the consumer assistants' mistake: Connecting an agent with an employee's username and password is exactly what triggered the banks' reaction. Fix: a dedicated service account with a limited role.
- All-or-nothing access: Many teams grant full access so the agent "doesn't get stuck". Fix: start with minimal permissions and expand them based on performance evidence.
- Sacrificing oversight for speed: Removing the approval step may save a few minutes, but a single wrong transaction can cost many times more.
- Sending sensitive data to external servers: Connecting public cloud agents to financial data raises leakage risk. On-premise model deployment removes that risk.
- No event memory: Without complete logs, nobody can prove after an incident whether the fault lay in the user's instruction or the agent's interpretation.
Questions Leaders and Users Are Asking About Financial AI Agents
Is it safe to give my banking password to an AI assistant?
No. Handing your password to any third-party software gives it full control of your account and may void your bank's fraud protection. The safe approach is to use official, tokenized connections offered by the bank itself, which grant limited access and can be revoked at any time.
Does this mean the end of AI agents in financial services?
Not at all. Banks are building their own internal agents for cash management and customer service. What has ended is unregulated agent access through customer passwords. The future belongs to agents that enter through an official gateway, with scoped permissions and human oversight built in from day one.
What should organizations outside the US learn from this?
As open banking, banking APIs and fintech platforms spread worldwide, the same challenge will reach every market. Organizations that design an official agent gateway, permission separation and full event logging today will capture the competitive advantage of intelligent automation instead of being forced to shut their doors.
This is the approach we follow in the DigiNoron Enterprise AI Transformation Model: agents are deployed on the organization's own infrastructure, with defined identity and authority, under human supervision. If you are interested in agents beyond finance, see our guide to AI-powered marketing department transformation.
Bring Agents In Through the Front Door, Not the Back Door
DigiNoron specialists design and implement secure agent gateways, permission separation, human approval workflows and on-premise model deployment for your financial and operational systems, so you gain the speed of automation without losing control.
Frequently Asked Questions About AI Agents in Banking
1. Which banks have blocked AI agents?
According to reports, JPMorgan Chase, Bank of America, Wells Fargo, Citigroup, Morgan Stanley and Charles Schwab are among the institutions that have restricted or blocked third-party agents logging in with customer passwords, while simultaneously developing controlled, read-only access paths for approved AI tools.
2. What does the Section 1033 open banking rule say?
Finalized in October 2024, the rule requires banks to share a customer's financial data, at the customer's request, with authorized providers through secure, standardized interfaces, phasing out password-based data scraping. Its implementation has been stalled by litigation and the regulator's reconsideration.
3. What is the difference between screen scraping and tokenized access?
With screen scraping, software logs in with the user's password and gets full access. With tokenized access, the user grants consent inside the bank's own environment and the software receives a temporary, scoped key that can be revoked at any time, so the password never reaches the third party.
4. What does "human in the loop" mean for financial agents?
It means the agent can analyze, recommend and draft a transaction, but sensitive, irreversible actions such as transferring funds execute only after explicit approval from an accountable human. This mechanism both prevents agent errors from reaching production and makes liability unambiguous.
5. How can my organization connect agents to ERP and finance systems without security risk?
By giving each agent a distinct identity, separating read and write access, building an official gateway based on tokens or an internal MCP server, requiring human approval for financial actions, logging every event and deploying models on-premise. DigiNoron implements this architecture as a dedicated project.
About the Author and Technical Authority:
DigiNoron Specialist Team — 5+ Years of Enterprise AI Projects
The DigiNoron Enterprise AI Division brings together university faculty and industry data engineers to design and deploy intelligent agents and the secure architectures that connect them to enterprise systems, across petrochemical plants, water utilities, urban management and large commercial enterprises.
DigiNoron Specialist Team
5+ Years of AI Project Experience